


Introduction: Why Group Management Matters in Linux
Role-based access control and collaborative directory sharing in any multi-tenant Linux deployment hinge on well-structured group architectures. Rather than assigning privileges to individual accounts piecemeal, system administrators rely on security groups to delegate file ownership, daemon execution rights, and administrative capabilities. This walk-through covers how Ubuntu handles group provisioning via the Debian-native addgroup command-line utility, detailing standard workflows, custom group allocation, and the underlying records tracked inside /etc/group and associated system databases.
Getting Started with addgroup: Creating Standard User Groups
Before provisioning new groups, ensure the underlying utility is available on your host. On standard Debian/Ubuntu installations, addgroup ships within the core adduser package; if absent in minimal container footprints, install it via the package manager.
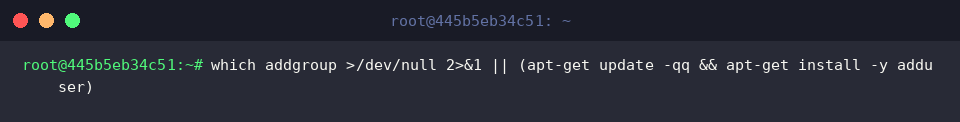
Invoking addgroup creates an entry in the system group database. Executed without extra flags, the utility scans existing GID records and automatically reserves the next available identifier within the standard, unprivileged range.
⚙️ [Essential Command-Line Options]
--gid GID : Explicitly binds the new group entry to a chosen numerical identifier.--system : Provisions a low-GID operational group dedicated to system services and daemons (typically below 1000).--quiet : Suppresses informational status output during execution.--debug : Prints verbose diagnostics detailing internal variable assignments and script execution steps.--force-badname : Bypasses strict POSIX group naming restrictions, permitting special characters.
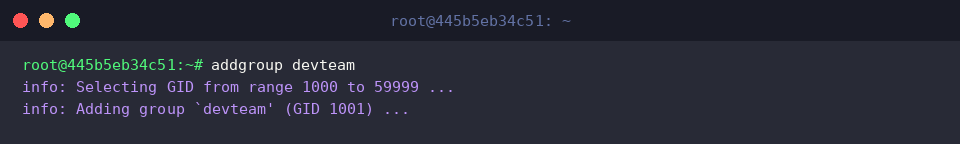
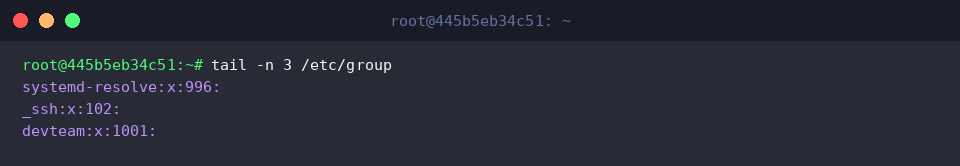
Confirm that the new entry was appended to the primary group registry by inspecting the end of /etc/group with tail -n 3 /etc/group. The devteam entry should now appear alongside its newly issued GID.
Customizing Group IDs and Provisioning System Accounts (–system)
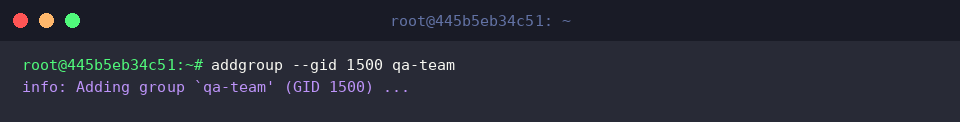
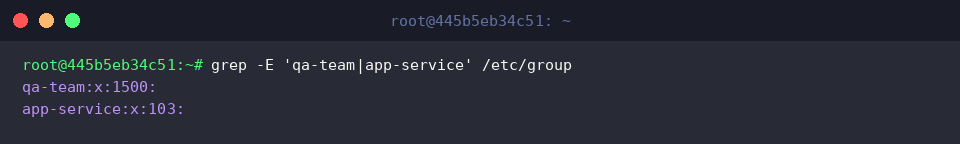
Organizational policies or network-attached storage permissions frequently require deterministic GID mapping across servers. Supplying --gid overrides automatic numbering, ensuring the created group receives an exact numerical ID—in this case, assigning 1500 to qa-team.
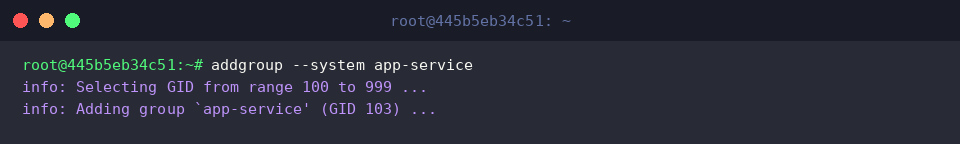
Background services, monitoring agents, and system daemons require isolated privileges without mingling with interactive human accounts. Passing the --system flag instructs the utility to pull from the reserved system pool (IDs between 100 and 999), assigning app-service a vacant low-numbered GID like 103.
A targeted regular expression query against /etc/group confirms the distinct GID allocations: qa-team adopts user-tier identifier 1500, whereas app-service resides within the privileged lower namespace at 103.
Managing Group Memberships and Verifying User Credentials
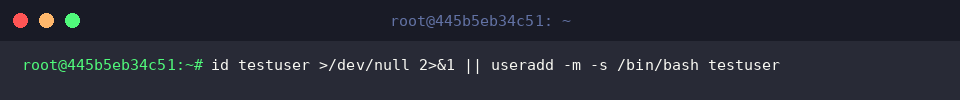
To demonstrate adding secondary memberships, set up an unprivileged test subject. The snippet below confirms whether testuser exists, creating a standard home directory and bash environment if the account is missing.
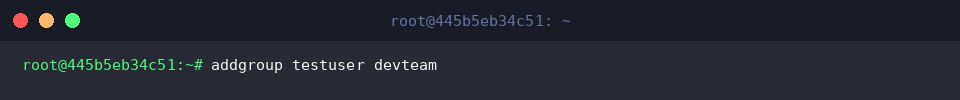
addgroup doubles as a membership assignment tool when supplied with both an existing user and target group argument. Calling addgroup testuser devteam appends the account to the secondary group without altering its primary login GID.
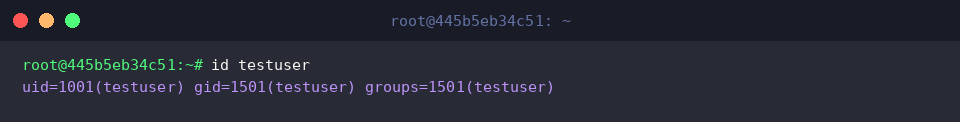
Inspect the effective identity mappings with id testuser. The output verifies the primary UID and GID alongside the secondary group list, confirming successful inclusion in devteam.
Under the Hood: Configuration Files and Database Structures
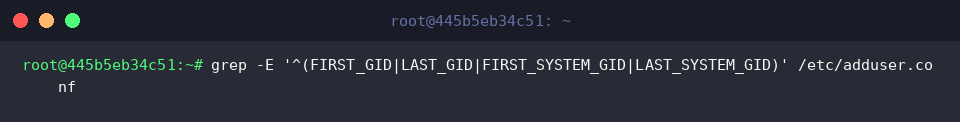
The selection logic that addgroup uses is determined by parameters in /etc/adduser.conf. Querying this configuration file reveals the numerical boundaries governing both system-level daemon pools and interactive user pools.
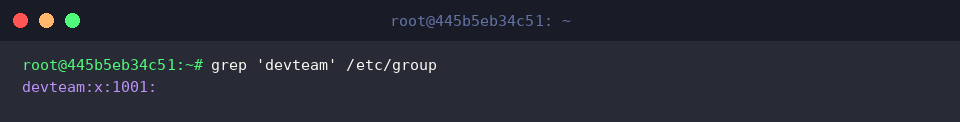
Examine the raw record stored in /etc/group for devteam. Standard entries follow a colon-delimited four-field structure: group name, password placeholder flag (x), assigned numerical GID (1001), and a comma-separated list of supplementary members.
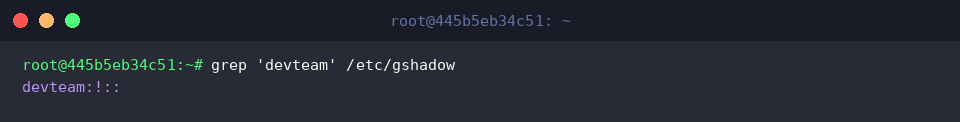
Administrative security attributes and group passwords reside in /etc/gshadow. Querying this restricted database shows the disabled password marker (!) alongside designated group administrators, providing an extra tier of isolation separate from the world-readable /etc/group file.
Mastering addgroup and its underlying database backends provides a robust foundation for building maintainable, least-privilege security boundaries across Ubuntu infrastructure.