


Overview
Modern Linux administration frequently requires translating binary data or sensitive text strings into safe, transferable ASCII characters. The standard base64 utility handles this translation seamlessly, safeguarding payloads from corruption when routed across legacy channels, network protocols, or configuration parsers. This guide walks through foundational stream processing, entire-file conversions, binary integrity verification, and production-ready formatting tricks tailored for Ubuntu environments.
String Encoding and Decoding via Standard Streams
The GNU coreutils base64 tool converts any input stream into Base64 format and reverses the transformation back to the original byte structure. Feeding stdout from commands like echo into base64 using standard shell pipes (|) yields an immediate ASCII representation.
⚙️ [Essential Command Flags]
-d, --decode : Reverses the Base64 transformation to retrieve raw input.-w, --wrap=COLS : Restricts line length by inserting newlines every COLS characters (use 0 to produce a contiguous single line).-i, --ignore-garbage : Instructs the decoder to discard unrecognized non-alphabet bytes during processing.
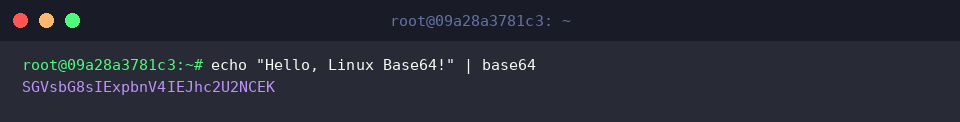
Supplying the --decode parameter reverses the encoded payload back to its original plain-text representation. Passing the previously generated token through the pipeline returns our original sentence, Hello, Linux Base64!.
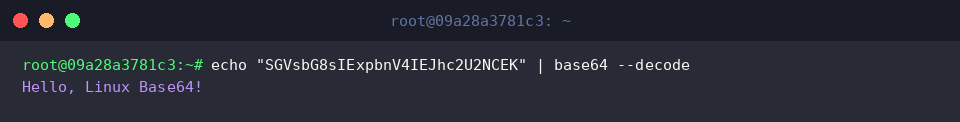
When transforming strings where trailing newline characters must not influence the resulting digest, pass the -n flag to echo. Omitting the trailing newline ensures precise token computation, typically denoted by terminating = padding characters.
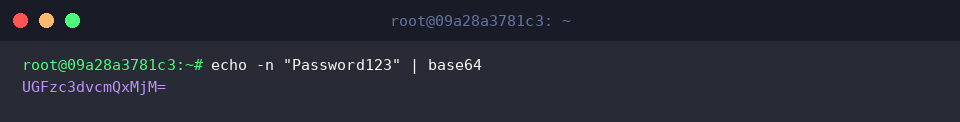
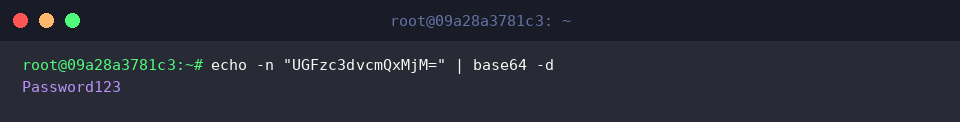
The short flag -d acts as an alias for --decode. Decoding the non-terminated token faithfully extracts the raw credential string without extra whitespaces.
Encoding and Restoring Entire Files
Direct filesystem operations do not require shell pipelines; base64 natively processes target files passed as arguments. Start by creating a mock text asset named sample.txt.
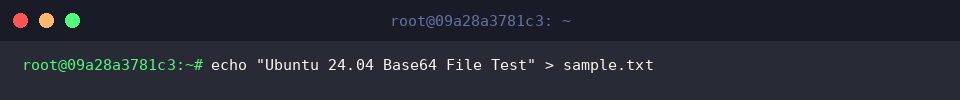
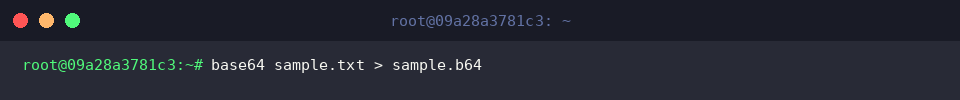
Pass the source path to base64 and redirect stdout via > into sample.b64 to store the encoded content on disk.
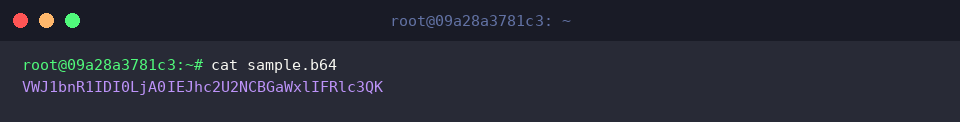
Inspect the artifact with cat to confirm that the text has been successfully structured into standardized ASCII blocks.
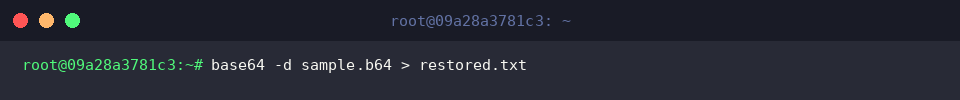
To unpack the file back to its native state, pass -d alongside the encoded file path, redirecting the restored stream into restored.txt.
A quick review of restored.txt confirms that the original text structure remains intact with zero byte distortion.
Processing Binary Payloads and Verifying Data Integrity
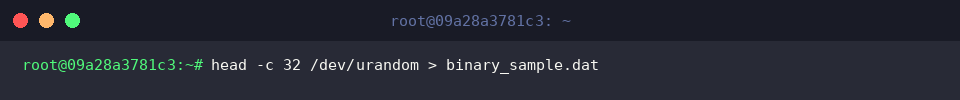
Base64 proves especially indispensable when shuttling binary files across text-bound network protocols. Generate an arbitrary 32-byte pseudo-random binary payload from /dev/urandom and save it as binary_sample.dat.
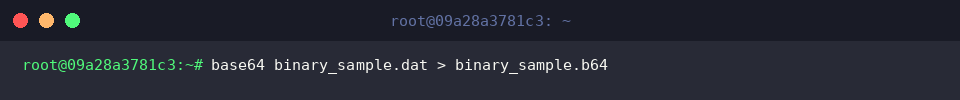
Execute base64 directly against binary_sample.dat and capture the resulting ASCII output within binary_sample.b64.
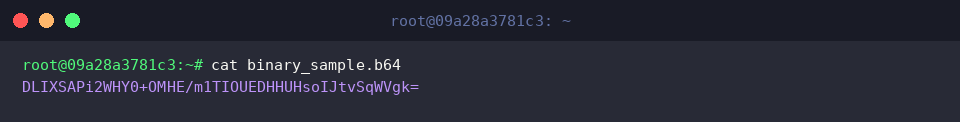
Inspecting binary_sample.b64 demonstrates how raw binary bytes convert cleanly into safe printable characters suitable for JSON payloads or XML blocks.
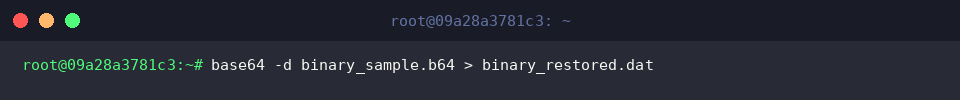
Reverse the binary file back into its raw state by issuing -d against binary_sample.b64, directing output to binary_restored.dat.
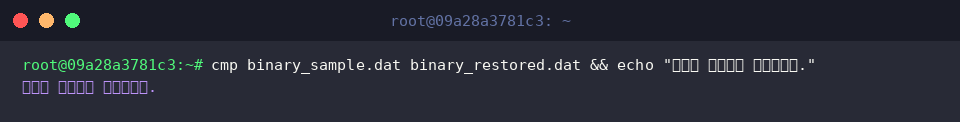
Audit the files byte-for-byte with the cmp utility. When the command executes silently without reporting offset mismatches, bit-level integrity is verified.
Preventing Line Wraps for Cloud Secrets and API Payloads
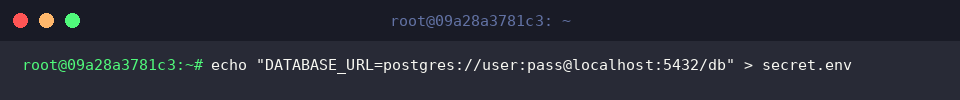
Standard base64 executions enforce line wrapping after every 76 characters by default. However, Kubernetes secrets, OAuth headers, and environment files require a strictly unbroken string. Create a sample connection configuration in secret.env to illustrate.
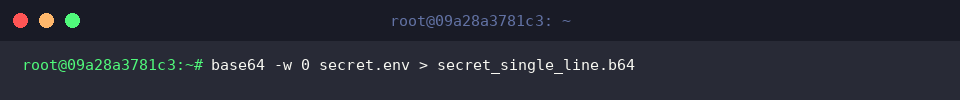
Incorporate the -w 0 flag into the invocation. This explicitly instructs the utility to suppress column wrapping and emit an uninterrupted single line into secret_single_line.b64.
Displaying the generated file with cat shows that no break characters interrupt the string, making it immediately copyable into cloud manifests or curl headers.
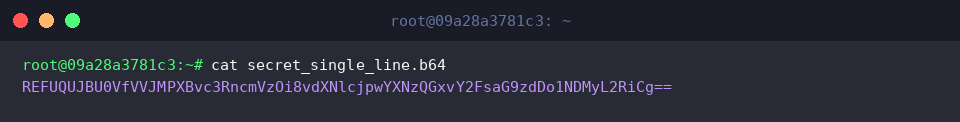
Because single-line exports omit trailing newlines, the bash prompt will attach directly to the output. Running an empty echo command resets the prompt cleanly to a new line.
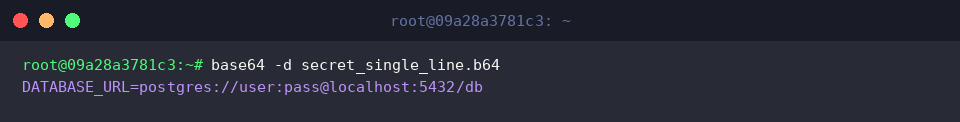
Reverting single-line payloads follows the identical -d syntax. The recovered connection string outputs cleanly without missing tokens or corrupt schema keys.
From quick terminal one-liners to automated CI/CD secret provisioning, mastering base64 ensures consistent data encoding across all stages of systems administration and software deployment.